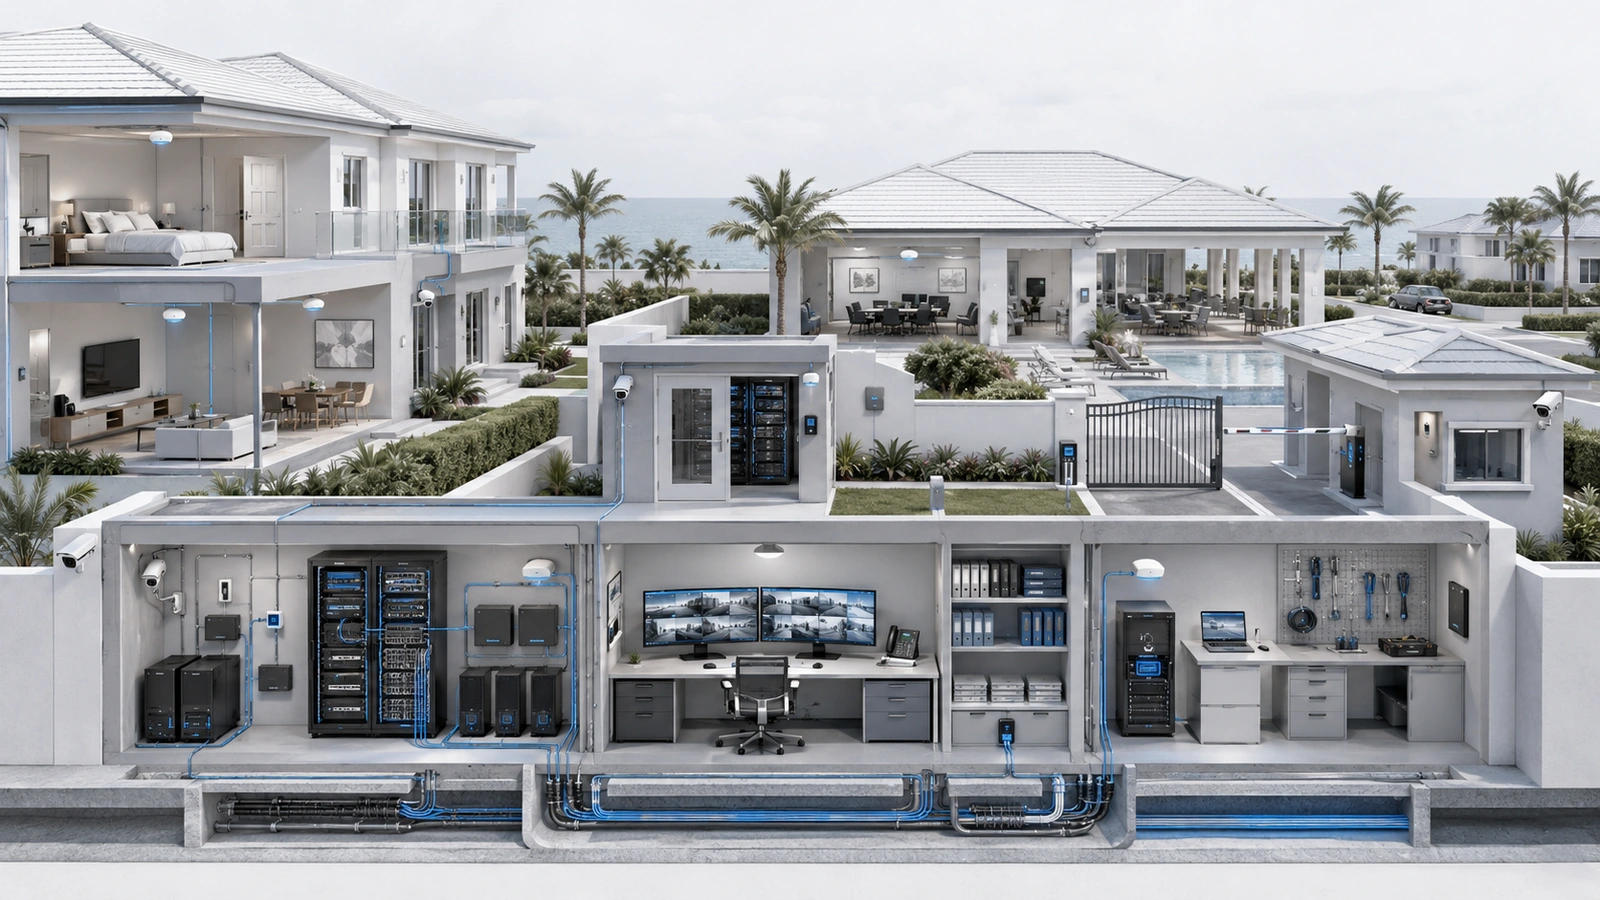
Reliable network infrastructure requires more than capable equipment and a competent original installation.
Over time, people change, vendors rotate, systems expand, credentials move between teams, configurations drift, and temporary fixes become permanent. Without clear operational rules, even a well-designed residential or community network can become difficult to support and recover.
Operational policy provides the structure that prevents this gradual decline. It defines who may make decisions, how access is controlled, what must be documented, how changes are handled, and what happens when normal operations fail.
The framework does not need to resemble enterprise bureaucracy. It needs to be proportionate, understandable, consistently followed, and appropriate to the property’s operational risk.
01 Understand the Difference Between Policies and SOPs
Policies and standard operating procedures serve different purposes and should not be treated as interchangeable documents.
- Policy establishes the rule, objective, authority, and expected outcome.
- Standard defines the minimum technical or operational requirement that must be met.
- SOP explains the approved steps for performing a recurring task.
- Technical record documents the property’s actual equipment, configuration, accounts, dependencies, changes, and history.
For example, a change-management policy may state that significant network changes require approval, documentation, testing, and a recovery plan. The corresponding SOP explains how to submit, evaluate, schedule, implement, verify, and close a change.
A configuration backup standard may define which systems must be protected, how frequently backups are required, and how they must be secured. A restoration procedure then explains how authorized personnel recover a particular device.
Keeping these document types distinct makes the framework easier to maintain. Policies remain relatively stable, while SOPs and technical records can evolve as equipment and workflows change.
02 Every Operational Document Needs Governance
A policy stored in a forgotten folder does not provide meaningful operational control. Every approved document should make its authority and current status clear.
At minimum, record:
- Document title and purpose
- Systems, locations, users, or activities within scope
- Document owner
- Approving authority
- Effective date
- Current version
- Last review and next review dates
- Related procedures, standards, and records
- Approved exception process
Responsibility should also be separated clearly. A property manager may own the operational process, a qualified technology provider may perform technical work, and an HOA board or designated authority may approve major policy or budget decisions.
Exceptions will occasionally be necessary, but they should not become invisible workarounds. An exception should record its reason, risk, approval, compensating controls, duration, and responsible owner.
Policies must also remain accessible to the people expected to follow them. Sensitive technical records may require stronger restrictions than general operational procedures, but authorized teams must still be able to retrieve them during outages and transitions.
03 Establish the Minimum Operational Policy Set
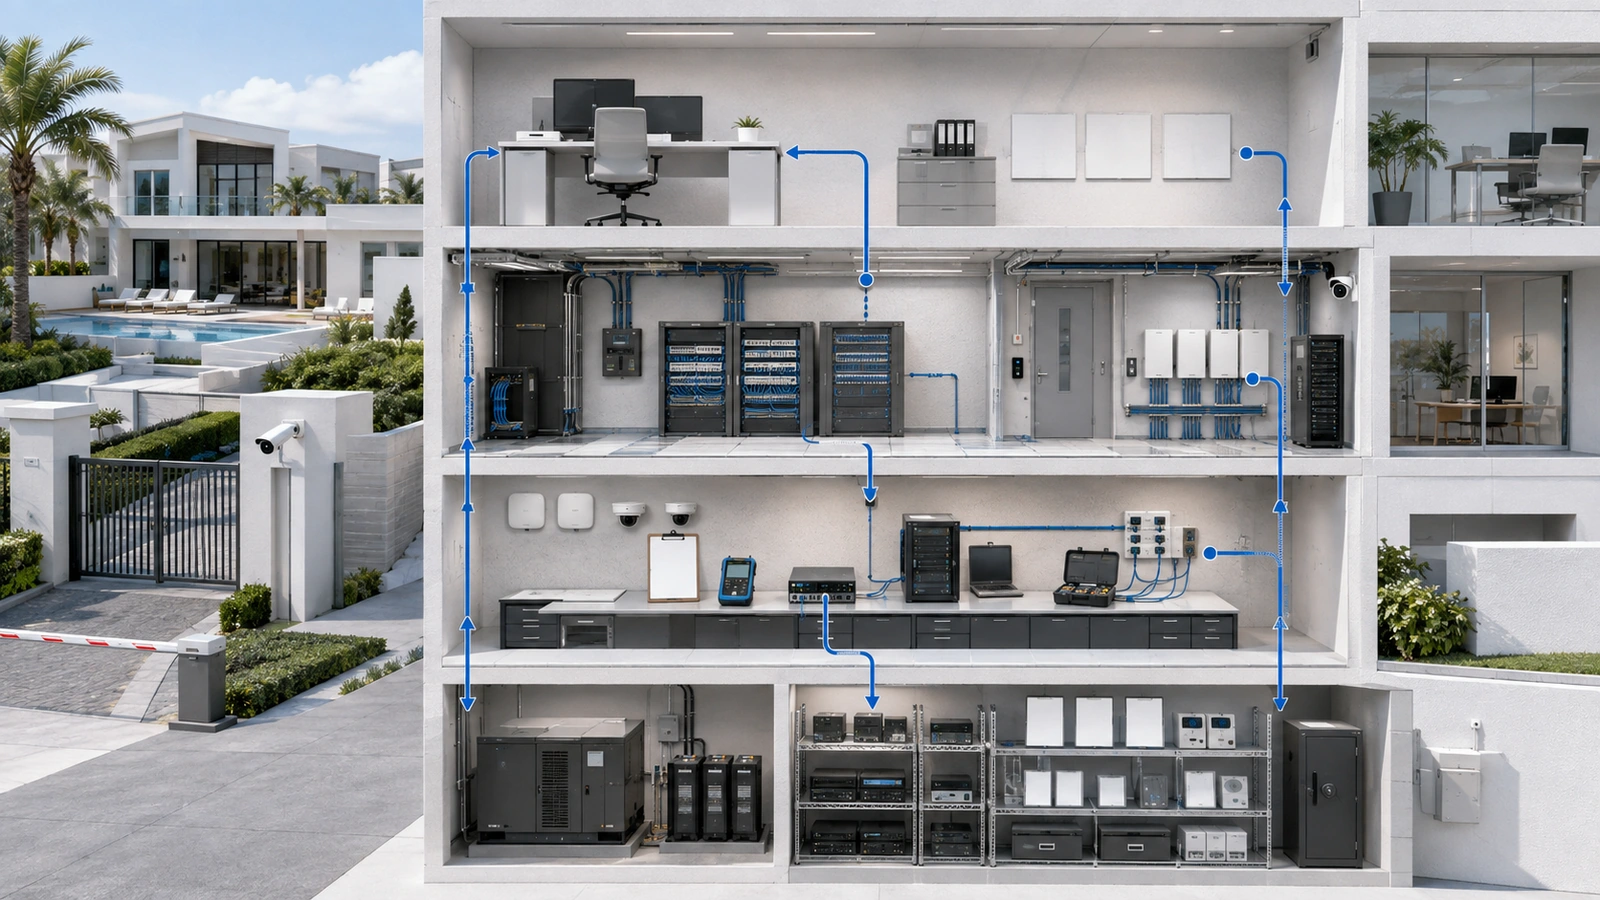
Not every property needs the same document library, but most residential and community environments benefit from several foundational control areas.
| Control Area | Policy Should Establish | Supporting SOP or Record |
|---|---|---|
| Administrative access | Who may access systems and under what conditions | Provisioning, review, recovery, and offboarding procedure |
| Network changes | Which changes require approval and validation | Change request, backup, test, rollback, and closure process |
| Documentation | What records must exist and who maintains them | Inventory, diagrams, change history, and review schedule |
| Vendor access | How third parties receive controlled access | Authorization, access activation, supervision, logging, and removal |
| Backup and recovery | Which configurations and records require protection | Backup verification and restoration procedures |
| Incident response | How disruptions and security concerns are classified and managed | Identification, containment, recovery, communication, and review |
| Guest and connected-device use | Who may connect, to which service, and under what expectations | Credential, onboarding, separation, support, and enforcement procedures |
The complete minimum policy set is explored in Basic Network Policies Every HOA or Residential Property Should Have.
These controls should reflect the services the property actually provides. A private home with one gateway requires less formal administration than a gated community supporting surveillance, access control, staff networks, guest Wi-Fi, remote vendors, and multiple shared facilities.
04 Protect Administrative Ownership and Access
Administrative access should never depend entirely on one employee, board member, installer, or outside vendor.
The property should retain practical ownership of critical systems even when daily administration is delegated to a qualified provider.
An access policy should define:
- Which roles may receive administrative, limited, or read-only access
- Who approves access
- How user identity is verified
- When multifactor authentication is required
- Where credentials and recovery information are stored
- How privileged activity is logged where supported
- How frequently access is reviewed
- How access is removed after role or vendor changes
Credentials should not be embedded in network diagrams, ordinary policy documents, tickets, or broadly shared spreadsheets. They should be maintained in an approved, access-controlled credential vault with a documented recovery method.
Named accounts are preferable to shared identities where systems support them because they improve accountability and allow one person’s access to be removed without disrupting everyone else.
Where a shared emergency account is operationally necessary, its use should be controlled, protected, monitored where possible, and reviewed after activation.
05 Control Changes Without Creating Bureaucracy
Unrecorded changes are a common source of instability. A firewall rule is modified, a switch is replaced, an access point is moved, or a vendor introduces remote connectivity without updating the property’s records.
Change control creates a deliberate path from proposal to verified operation.
A practical process should address:
- What will change and why
- Which systems, users, and locations may be affected
- Who is authorized to approve the work
- When the change should occur
- What configuration or state must be backed up
- How successful implementation will be verified
- How the previous state will be restored if the change fails
- Who must be notified before and after the work
- Which documentation must be updated
Routine, low-risk tasks may use preapproved procedures. High-impact changes require stronger planning, communication, and recovery preparation. The process should become more rigorous as potential operational impact increases.
Emergency work may require immediate action before normal approval is possible. It should still be authorized by the appropriate available person, documented during or immediately after the event, validated, and reviewed once the emergency has passed.
The supporting workflow is covered in How to Create a Simple Network Change Management Process.
06 Make Documentation and Backups Recoverable
Documentation allows the property to understand its infrastructure. Backups allow authorized teams to restore selected systems without rebuilding them entirely from memory.
Baseline technical records may include:
- Physical and logical network diagrams
- Equipment inventory and locations
- Internet circuits and provider information
- Network segments and their purposes
- Important cable, fiber, switch-port, rack, and power relationships
- Vendor contacts, responsibilities, contracts, and licenses
- Critical system dependencies
- Remote-access methods and account ownership
- Change history and known limitations
- Recovery procedures and approved configuration backups
The documentation set should identify one authoritative location, an owner, version information, and a review date. Sensitive records should be encrypted and access-controlled according to their risk.
Configuration backups should be stored separately from the device being protected. Where technically appropriate, they should be versioned and validated through a controlled restoration test or another reliable recovery check.
A backup that cannot be located, decrypted, interpreted, or restored by authorized personnel provides limited protection.
Detailed documentation guidance is available in Network Documentation Best Practices for Homes, HOAs and MDUs.
07 Govern Vendors as Authorized Participants
Residential and community infrastructure frequently depends on internet providers, surveillance contractors, access-control integrators, automation specialists, managed network providers, and other third parties.
Vendor expertise may be essential, but access should be based on approved operational purpose rather than convenience alone.
Vendor governance should define:
- The systems and locations the vendor may access
- The purpose and duration of that access
- The approved onsite and remote-access methods
- Required authentication and named identities
- Whether activity records are available and reviewed
- Who authorizes work and technical changes
- What documentation and configuration must be delivered
- How access is suspended or removed
- What happens when the vendor relationship ends
Persistent access may be justified for an approved managed service, but it should remain documented, secured, reviewable, and limited to the required scope. Temporary work should not quietly create permanent remote-access paths.
The property should also understand any vendor-created accounts, cloud dependencies, licensing relationships, configuration ownership, and data-export limitations.
The dedicated guide will use the cleaned URL: Vendor Access and Third-Party Network Risks in HOA Networks. The former URL ending in -2 should permanently redirect to this address.
08 Prepare for Incidents, Maintenance, and Communication
Operational policy becomes most valuable when normal conditions are disrupted.
An incident-response structure should define:
- What qualifies as an operational or security incident
- How severity and impact are classified
- Who leads technical and operational response
- Who has authority to contain affected systems
- What evidence should be preserved
- When vendors, management, leadership, or other parties are notified
- Who communicates with residents or stakeholders
- How recovery is tested and confirmed
- How lessons and corrective actions are recorded
Incident response should distinguish containment from recovery. Disconnecting or isolating a system may limit harm, but the property must still establish how essential service will be restored safely and how normal operation will be verified.
Planned maintenance requires a similar communication structure. Shared properties should define approved work windows, expected notice, affected services, support contacts, rollback preparation, completion confirmation, and escalation if the maintenance exceeds its window.
Communications should describe confirmed impact and next steps without making unsupported promises about restoration time or disclosing sensitive technical information.
The detailed response process appears in Incident Response Basics for Residential and HOA Networks.
09 Scale and Review the Framework
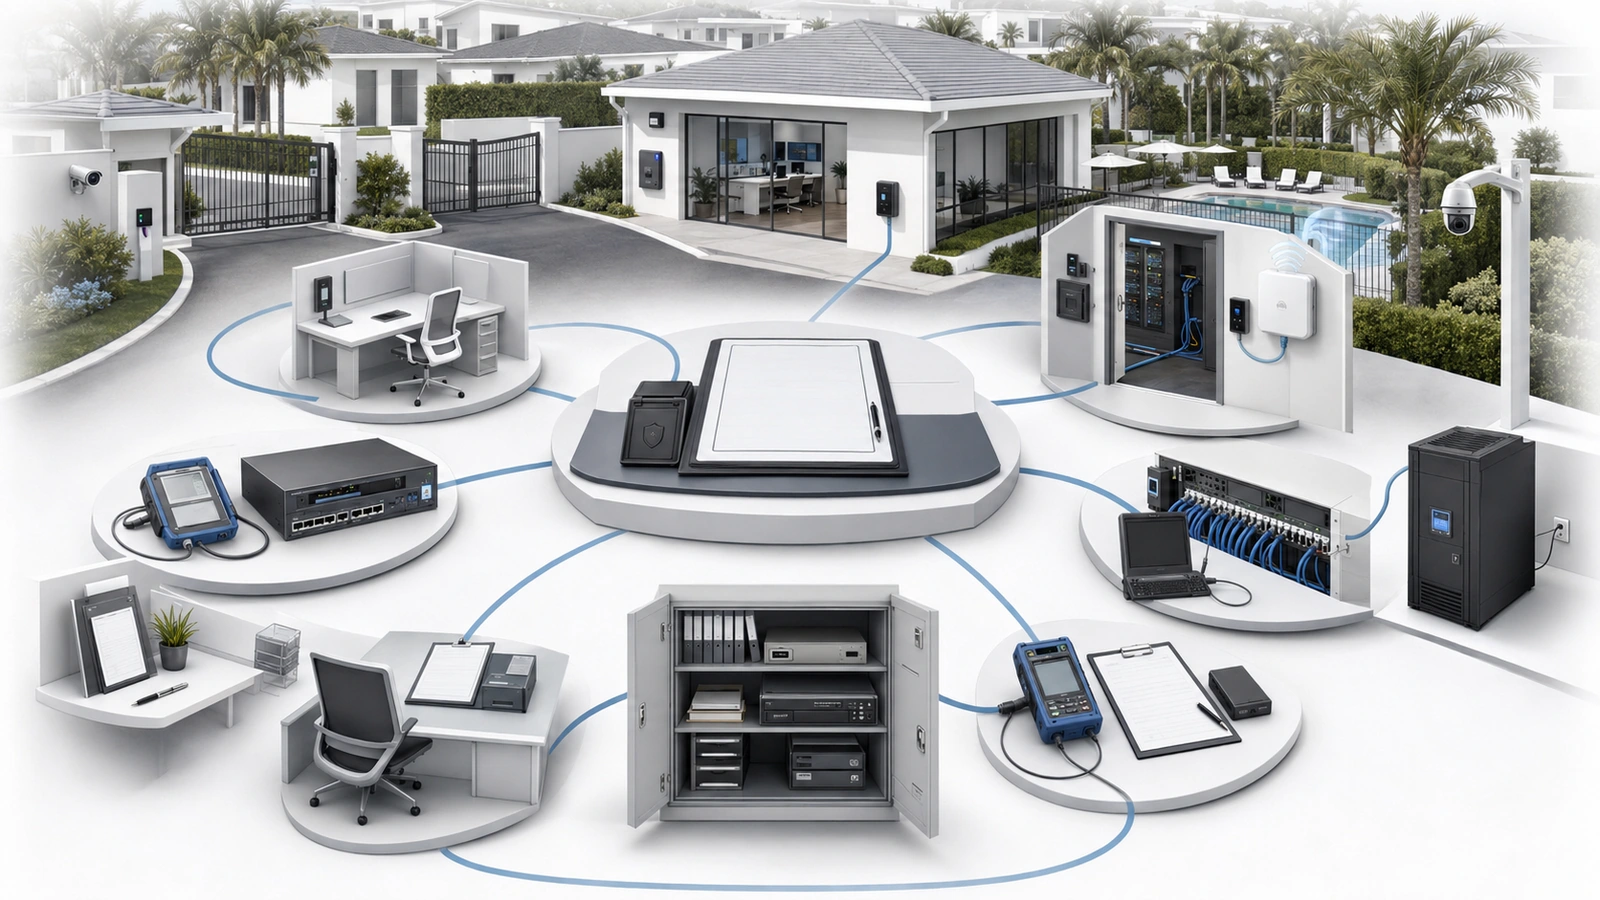
The same principles apply across different property types, but the degree of formality should reflect the environment.
A private residence may maintain a concise set of records covering administrative ownership, internet service, equipment, Wi-Fi networks, configuration backups, trusted support contacts, and recovery instructions.
An HOA or gated community may require approved vendor-access rules, documented maintenance windows, role-based administration, change authorization, incident escalation, resident communication, guest-network expectations, and centralized records.
A high-rise or MDU may require additional coordination across management, multiple technology spaces, backbone infrastructure, access-controlled rooms, shared services, specialist vendors, and systems affecting many occupants.
Operational Framework Review Checklist
- Confirm that each policy has a current owner, approver, version, and review date.
- Verify that supporting SOPs reflect the property’s actual systems and responsibilities.
- Review administrative, staff, emergency, and vendor access.
- Confirm that credentials and recovery information remain securely accessible.
- Reconcile diagrams and inventories with installed infrastructure.
- Review recent changes and confirm that documentation was updated.
- Verify configuration backups and applicable recovery procedures.
- Review vendor scope, remote-access methods, licenses, and offboarding readiness.
- Test incident contacts, escalation paths, and communication procedures.
- Review guest-network and connected-device expectations.
- Record approved exceptions and remove those no longer required.
- Assign corrective actions, owners, priorities, and target dates.
Review frequency should reflect change volume and operational importance. A stable private-home environment may be reviewed after significant changes and periodically thereafter. A shared property with frequent vendor activity and critical services may require more structured recurring reviews.
Policies should also be simplified when they stop serving a clear purpose. An elaborate process that nobody follows provides less protection than a concise, enforceable process incorporated into daily work.
Final Perspective
Infrastructure does not remain reliable through equipment quality alone.
Long-term stability depends on who owns the environment, who may access it, how changes are controlled, what information is preserved, how third parties are governed, whether configurations can be recovered, and how the property responds when something goes wrong.
Operational policy creates that structure. SOPs turn the structure into repeatable action, while accurate technical records preserve the actual state of the environment.
The goal is not administrative complexity. It is a practical operating system for the property’s technology—clear enough to follow, secure enough to trust, and durable enough to survive changes in people, vendors, equipment, and leadership.